Why Local-First Chrome Extensions Are Safer for Customer Data Than Cloud Tools
The Customer Data Problem with Cloud Tools
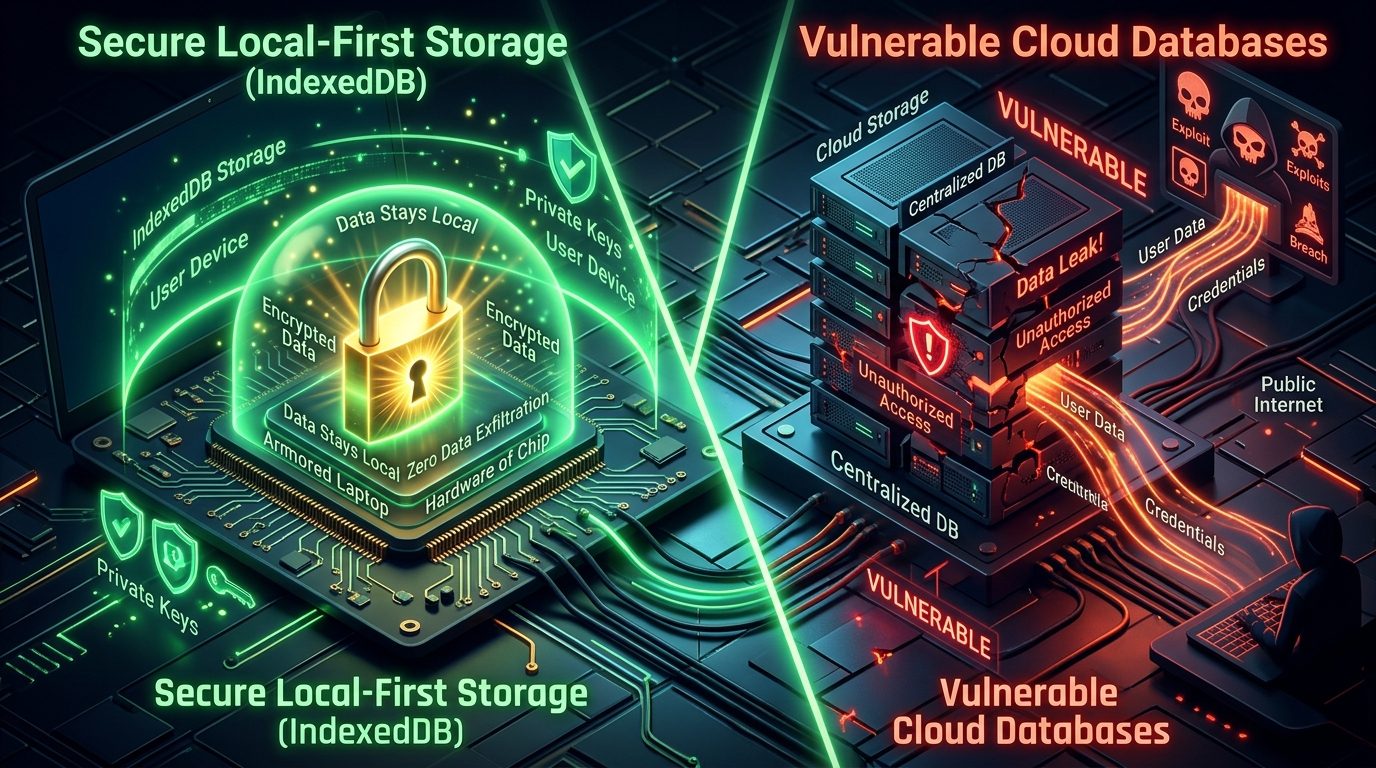
Most WhatsApp bulk messaging tools — both legitimate and illegitimate — require you to upload your customer contact list to their cloud servers. Once uploaded, your data lives on infrastructure you don't control, processed by code you can't audit, accessible by employees you've never met. Here's what can go wrong:
- Data breaches: Cloud servers are targets for hackers. A single breach can expose thousands of businesses' customer data simultaneously.
- Unauthorized selling: Some tools sell customer contact data to third-party data brokers or marketing companies as a side revenue stream.
- Insider access: Employees of the tool company can access your customer data without your knowledge or consent.
- Subpoena and government access: Data stored on servers can be subject to government requests, legal discovery, or law enforcement access.
- Service shutdown: If the tool company shuts down, your data may be sold as an asset, archived insecurely, or exposed during liquidation.
- No audit trail: You have no way to know who accessed your data, when, or for what purpose.
Small businesses often lack the legal resources to pursue cloud tool providers for data misuse. Once your customer list is on someone else's server, you've lost control of it permanently.
What Is Local-First Architecture?
Local-first is a software architecture principle where all data is stored on the user's device — not on any external server. The application works entirely offline, and data synchronization (if any) is optional and user-controlled. In the context of a Chrome extension like SamparkWA, local-first means:
- All customer contact data is stored in the browser's IndexedDB local database
- No data is transmitted to any external server at any point
- No backend API or cloud database is involved in any operation
- The extension works fully offline (except for WhatsApp Web itself, which requires internet)
- The user has complete control over their data and can delete it at any time
Cloud Tools vs. Local-First Extensions
| Aspect | Cloud-Based Tools | Local-First Extensions (SamparkWA) |
|---|---|---|
| Data storage location | Third-party cloud servers | Your browser's IndexedDB |
| Data breach risk | High — servers are hacker targets | Near zero — no server to breach |
| Data selling risk | Possible — no transparency | Impossible — no server access |
| Insider access | Yes — company employees can access | No — data never leaves your device |
| Works offline | No | Yes (except WhatsApp Web itself) |
| Audit trail | None — you can't see who accessed | Full — it's all on your device |
| Data deletion | Request-based, may not be honored | Immediate — clear browser data |
| GDPR/DPDP compliance | Complex — requires DPAs and audits | Simple — data never leaves device |
| Cost | Monthly subscription | Free |
How IndexedDB Keeps Your Data Local
IndexedDB is a browser-native database that Chrome, Brave, Edge, and other Chromium browsers provide for storing structured data locally. SamparkWA uses IndexedDB for:
- Contact database: All imported CSV contacts with validation status
- Template library: Saved message templates in all supported languages
- Opt-out registry: Phone numbers that have been excluded from campaigns
- Campaign history: Records of past campaigns with send status per contact
- Settings: Business name, default country code, language preferences
IndexedDB data is scoped to the extension's origin — no other extension, website, or application can access it. It persists across browser sessions and survives restarts. The only way to lose data is to explicitly clear browser data or uninstall the extension.
Trustoryx Security Standards
SamparkWA is engineered by Trustoryx, a digital verification and cybersecurity ecosystem. The local-first architecture is one of several security standards inherited from Trustoryx's engineering practices:
- Zero data exfiltration: No telemetry, no analytics, no error reporting that includes customer data
- Strict IndexedDB isolation: Extension data is sandboxed — no cross-origin access
- CSV formula injection defense: All imported cells are sanitized for =, +, -, @ prefixes
- E.164 validation: Phone numbers are validated before storage to prevent malformed data
- Chrome Manifest V3 compliance: Uses the latest, most secure extension platform
- Open auditability: The extension can be loaded unpacked, allowing anyone to inspect the code
SamparkWA can be loaded as an unpacked extension, meaning you can inspect every line of code before running it. No obfuscation, no minification-only distribution, no hidden network calls. See for yourself at https://samparkwa.trustoryx.digital/download